Document management
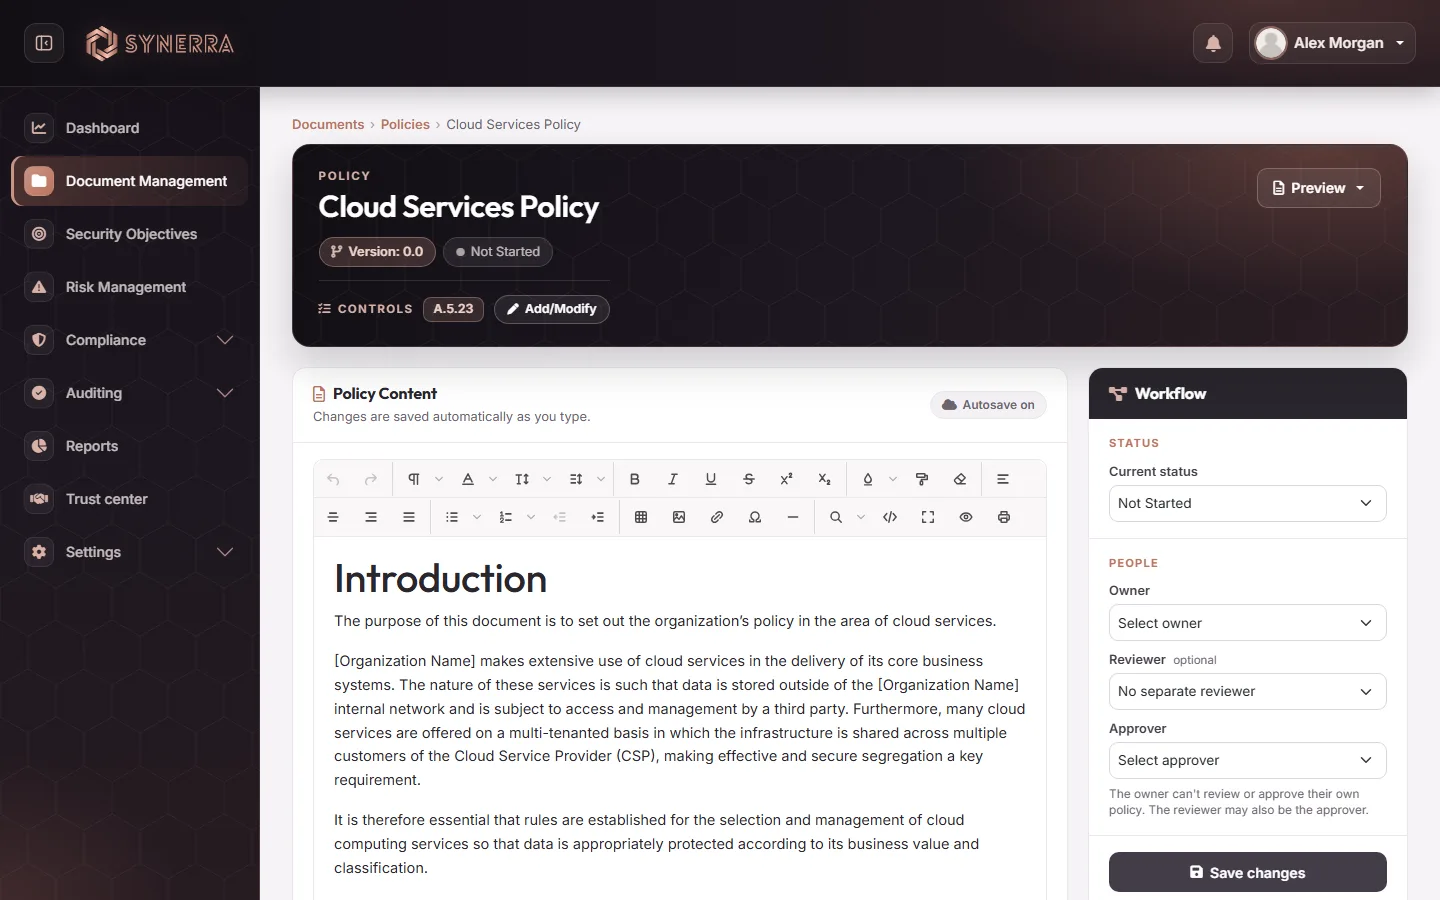
Policies and procedures with a Word-like editor, versions, owner / reviewer / approver workflow and annual revisions.
-Photoroom.png)
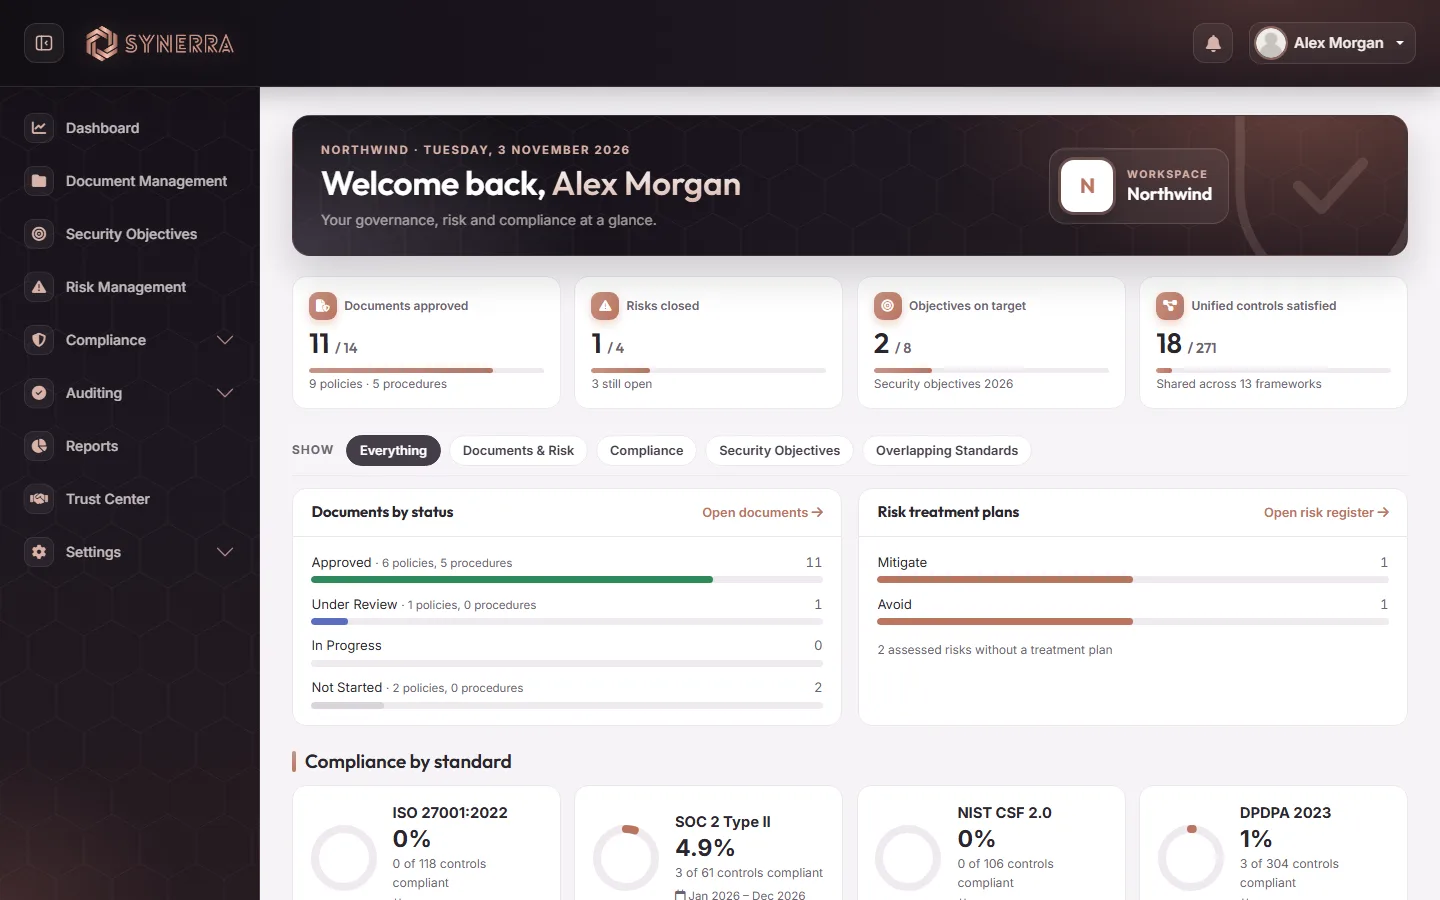
Synerra brings your policies, risk register, audits and frameworks — ISO 27001, SOC 2, DPDPA, NIST CSF and the ISO management standards — into one platform, so every control has an owner, evidence and a clear status.
Built for the standards your auditors ask about
Seven modules that share one set of people, controls and evidence — no spreadsheets passed around before an audit.
Policies and procedures with a Word-like editor, versions, owner / reviewer / approver workflow and annual revisions.
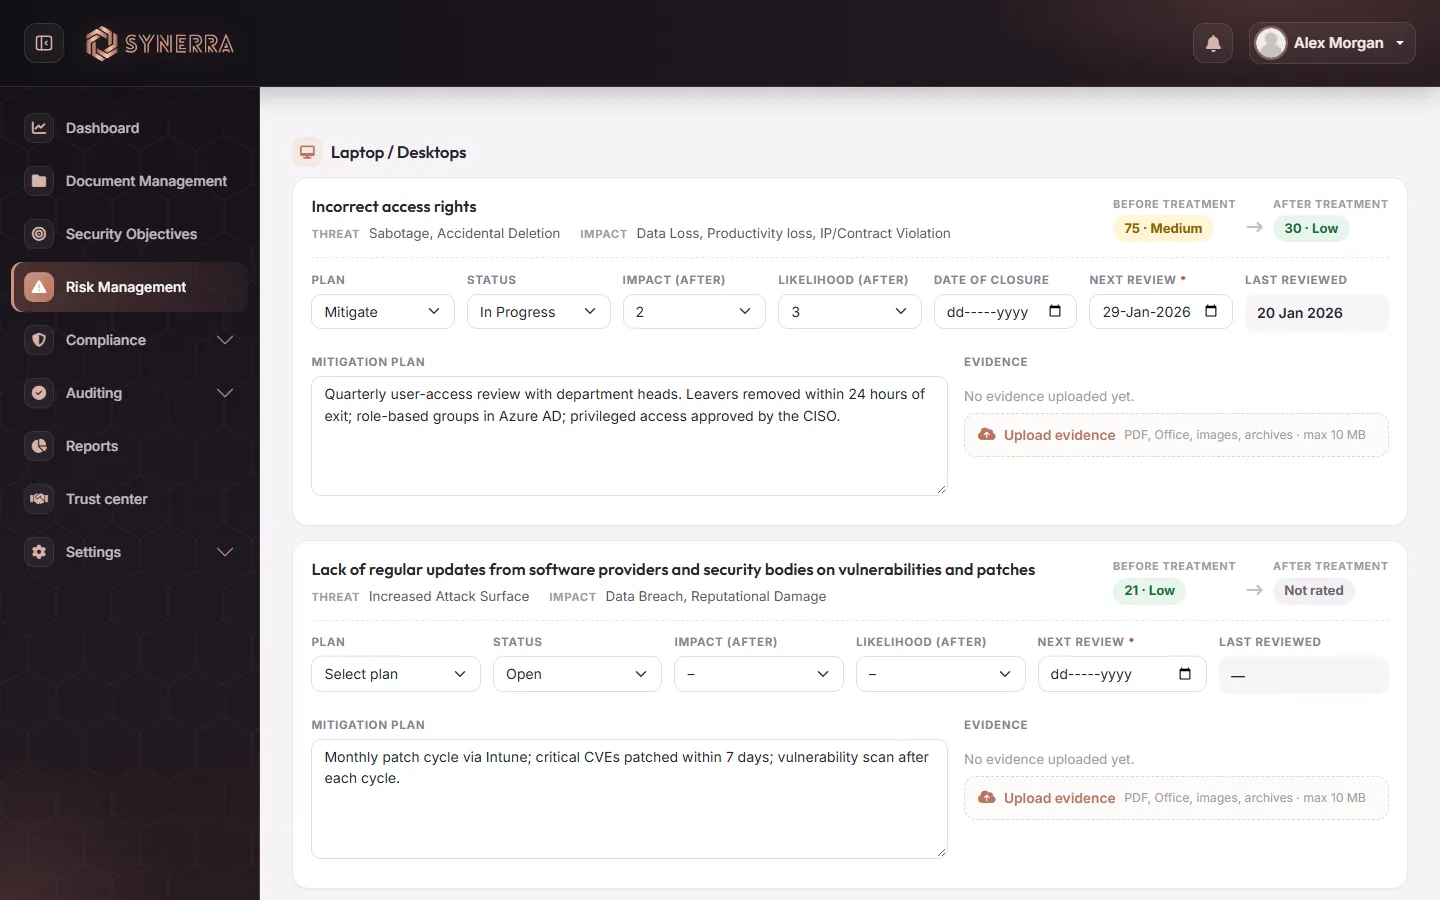
Score each asset's risks on confidentiality, integrity and availability, plan treatment, attach evidence and track the residual risk.
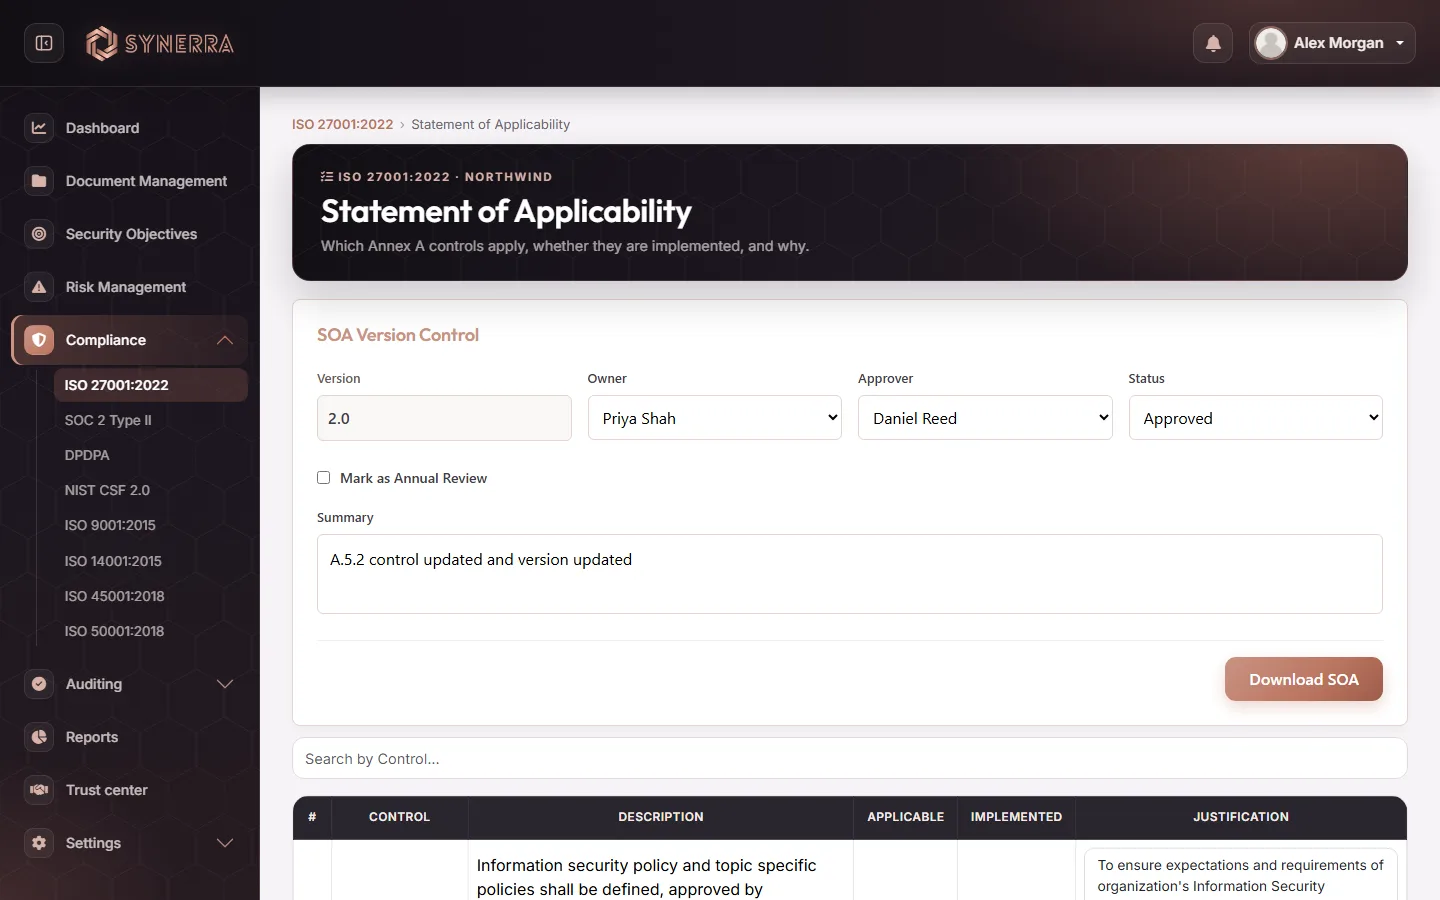
Control-by-control status and evidence for every standard, the Statement of Applicability and unified controls that count once.
Department audits with checklists, findings and evidence — Internal and External Auditors get their own view-only access.
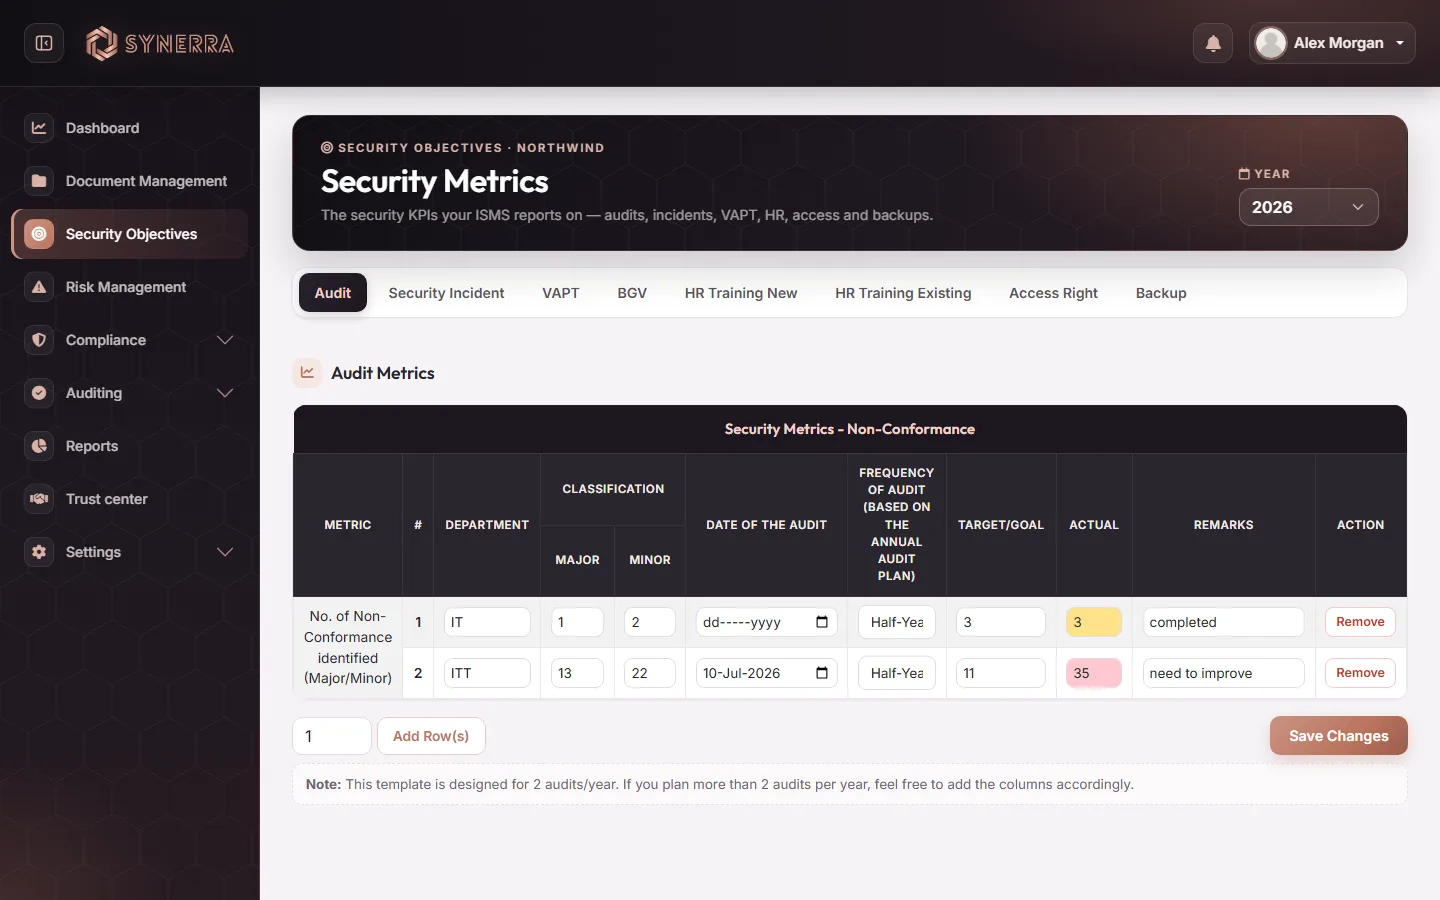
The KPIs your ISMS reports on: audits, incidents, VAPT, background checks, training, access reviews and backups.
Share selected policies and certificates with customers through invite-only, time-limited access — and answer security questionnaires.
SOC 2 report, risk register, Statement of Applicability and audit reports — exported to Excel and PDF when the auditor asks.
A walkthrough tailored to the standard you are working towards.
Book a demoEvery change is saved as you go, recorded in the audit trail and visible to the people who approve it.
Each risk shows its score before and after treatment. Plan, status, review dates, the mitigation plan and evidence sit together — and the register keeps a revision history with approvals, just like your SOA.
Draft in a familiar Word-like editor (paste straight from Word), assign an owner, reviewer and approver, and publish a new version only when it is approved.
Mark each Annex A control as applicable and implemented with its justification. Version control, annual reviews and an Excel export are built in.
Audit non-conformities, incidents, VAPT findings, background verification, training, access reviews and backups — per year, against target.
Choose your frameworks, invite your team and assign owners, approvers and auditors.
Write policies, score risks, plan treatment and collect evidence against each control.
Approve versions, run internal audits and export the reports your auditor and customers ask for.
The platform that holds your evidence is held to the same standard.
Authenticator-app MFA for every account, with Microsoft and Google sign-in.
Admins, users, and view-only Internal and External Auditors — each sees only their organisation.
Each organisation's evidence is kept in its own storage bucket.
Who changed what and when — before and after values — for every change.
Tell us where you are in your compliance journey and our team will set up a walkthrough for you.
Prefer e-mail? product@digialert.com